Small businesses have to protect important systems, accounts, and data without the same budget or technical resources available to larger organizations. That makes security more important than building a complicated stack of tools that no one has time to manage. Axiom Defender small business cyber security can be considered as part of a practical approach to managing these needs.
Antivirus software and strong passwords still matter, but they do not cover every way an attacker can get in. Phishing, ransomware, stolen credentials, and simple human mistakes can create very different security problems. A business needs to look at those risks together rather than treat each one as a separate technical issue.
This is where Axiom Defender fits into the discussion. Its role is considered here in terms of identifying security risks, supporting ongoing protection, and making security management more practical for a small business. The focus is on how those efforts fit into normal business operations, not on turning cybersecurity into another complicated project.
Why Small Businesses Need a Practical Cyber Security Approach
Limited resources can make security gaps easier to overlook. A small company may have one person handling IT alongside other responsibilities, or no dedicated cybersecurity staff at all. Software updates, account permissions, backups, and security monitoring can slip down the list when the business is busy. Axiom Defender small business cyber security is relevant to this discussion because practical security support can be particularly useful when internal resources are limited.
The idea that attackers only care about large companies can also create a false sense of safety. A small business still holds customer information, employee accounts, financial details, email access, and systems that may be useful to an attacker. The business does not have to be famous or large to have something worth taking.
The damage can extend beyond the initial compromise. A stolen account may expose company information or be used to impersonate an employee. A compromised system can interrupt normal work, while problems involving financial information can create costs that are harder to recover from.
Cybersecurity belongs in the same risk conversation as other things that can disrupt a business. The question is not whether a company can afford perfect security. It is whether the business has reasonable protections in place before a preventable problem disrupts operations. Axiom Defender small business cyber security should therefore be viewed within the wider security strategy rather than as a replacement for every security measure.
Waiting until an attack happens also puts more pressure on recovery. Some businesses can restore systems quickly; others may discover that backups, access controls, or response responsibilities were never properly prepared.
The Threats Small Businesses Actually Need to Understand
Phishing remains a practical problem because it targets people rather than trying to break through a technical control directly. An employee may receive a message that looks legitimate and be pushed to open a link, share information, or sign in somewhere they should not. Social engineering works in much the same way by manipulating trust or urgency.
Business Email Compromise can be especially damaging because the attacker may focus on money rather than data. A fraudulent payment request, an impersonated executive, or a message asking someone to change bank details can look routine when an employee is moving quickly.
Ransomware and other malware can create a more direct disruption. Files may become inaccessible, devices can be affected, and normal business work may stop while the company tries to regain control. The problem is not limited to the infected computer if shared systems or other connected resources are involved.
Weak, reused, or stolen credentials create another route into business accounts. Once an attacker has valid login information, the activity may look less suspicious than an obvious malware infection. This is one reason monitoring matters. A business has a better chance of responding early when unusual account or system activity is visible instead of being discovered after the damage is already done. Axiom Defender small business cyber security can fit into this broader need for ongoing awareness and security management.
What Effective Small Business Protection Looks Like
Effective protection starts with controls that reduce the most likely ways a business could be compromised. Multi-factor authentication adds another check beyond a password, while access controls limit who can reach particular accounts, systems, or information.
Software, applications, and devices also need regular updates. Leaving known security weaknesses unaddressed can create problems that are avoidable with basic maintenance.
Important business data needs reliable backups, but having backups is only part of the job. A recovery plan should make it clear what needs to be restored and how the business will get back to normal if systems become unavailable.
People remain part of the security process. Employees need enough awareness to recognize suspicious messages, unusual requests, and possible security incidents without having to become cybersecurity specialists. Requests involving payments or bank-detail changes deserve a separate verification step rather than relying on the message itself.
These measures also need regular attention. Security is not something a business sets up once and then leaves alone while its systems, employees, and day-to-day processes change. Axiom Defender small business cyber security can be considered alongside these ongoing practices when a business is reviewing how its security processes are managed.
How Axiom Defender Can Support Small Business Security
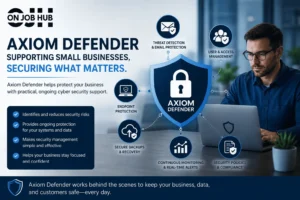
Axiom Defender supports a small business security strategy rather than replacing every part of it. Axiom Defender small business cyber security is best understood through the security work a business needs to keep up with, particularly when internal resources are limited.
Support for identifying security risks and weaknesses can help a business see where its existing protection needs attention. Axiom Defender small business cyber security may be relevant where a business needs support in understanding security risks and maintaining visibility over its environment.
The management side matters too. Security can become difficult to maintain when different tasks, alerts, and services require constant manual attention. Streamlined or automated processes may reduce some of that workload, although the right level of automation depends on how the business operates and what it needs to protect.
The useful question is therefore not whether Axiom Defender provides every security control a business could ever need. It is how its capabilities fit with the protections already in place and where they can help close practical gaps. Axiom Defender small business cyber security should be evaluated in that context rather than in isolation.
Matching Security Measures to Real Business Risks
A small business does not automatically need the same security setup as another company of the same size. Two businesses with ten employees can have very different exposure depending on the systems they use, the information they hold, and how they handle payments.
A useful assessment looks at the actual environment: users, devices, applications, business data, and processes that could create financial or operational risk. That makes it easier to put attention where a compromise would cause the most trouble. Axiom Defender small business cyber security can form part of that broader assessment when businesses consider where additional security support may be useful.
Priority matters because not every security task has the same impact. A business may have limited time and money, so high-impact weaknesses should be dealt with before lower-priority improvements that can wait.
Usability also has to stay in the picture. A security control that is difficult to manage or regularly gets bypassed may not provide much protection. The goal is to choose measures that fit the business well enough to be maintained without creating unnecessary disruption.
That makes the number of features in a security solution less useful as a deciding factor. What matters more is whether the protection addresses the business’s actual vulnerabilities and the risks that matter most to its operations. Axiom Defender small business cyber security is therefore most useful as a phrase describing the role of Axiom Defender within that practical security discussion.
Making Cyber Security Sustainable for a Small Business
A small business does not need to do everything at once. With a limited budget, it makes more sense to keep essential protections in place and improve weaker areas as resources allow. The approach has to be realistic enough that someone can actually maintain it.
Security responsibilities should also be clear. Even without dedicated cybersecurity staff, someone needs to know who handles access changes, checks security issues, follows up on alerts, and makes sure important processes do not get forgotten. Axiom Defender small business cyber security can be considered as part of this approach where outside security support helps supplement limited internal capacity.
Employee awareness, technical controls, and monitoring work better as parts of the same process. Relying too heavily on any one of them can leave gaps that become harder to notice over time.
The security posture should be reviewed regularly rather than treated as fixed. New employees, devices, applications, vendors, or changes in how the business handles information can change what needs attention.
Support from a service such as Axiom Defender can fit into that process, but it should not be treated as an automatic substitute for the wider security strategy. The business still needs to understand what it is protecting and how those responsibilities are managed. Axiom Defender small business cyber security should remain connected to those wider operational considerations.
Frequently Asked Questions
Are small businesses really attractive to cybercriminals?
Yes. Size alone does not determine whether a business is worth targeting. Business accounts, financial information, customer data, and access to company systems can all have value to attackers.
Is antivirus alone enough for a small business?
No. Antivirus can help protect devices from malicious software, but it does not address every security risk. Account security, employee awareness, access controls, backups, and monitoring also have a role. Axiom Defender small business cyber security is similarly part of a broader protection strategy rather than a replacement for these basic controls.
How important is MFA for a small business?
MFA is an important layer of account protection because a stolen password by itself is less useful when another authentication step is required. It is especially relevant for accounts that provide access to important business systems or information.
What type of support does Axiom Defender provide for small-business security?
Axiom Defender may support security risk identification, ongoing monitoring, and security management. The exact value depends on the business’s existing setup and security needs. Axiom Defender small business cyber security can therefore be assessed according to the specific requirements and existing controls of each business.
Can a business with limited IT staff manage effective cyber security?
Yes. Limited staff does not make effective security impossible, but it does make prioritization and clear responsibility more important. Businesses can focus on the protections that address their most important risks and use outside support where internal capacity is limited. Axiom Defender small business cyber security may be relevant when considering that additional support.
Which risks should a business prioritize first?
Start with risks that could cause significant financial, operational, or data-related harm. The priority should reflect the business’s actual systems, users, information, and processes rather than a generic checklist.
What to Keep in Mind
Small business cybersecurity is not about eliminating every possible threat. The goal is to identify important risks, reduce unnecessary exposure, and manage problems when they arise.
Effective protection depends on more than technology. Access controls, employee awareness, monitoring, and recovery planning all need to fit together well enough to support the way the business actually operates.
Axiom Defender’s value depends on whether its support addresses real security needs and fits the resources the business has available. Axiom Defender small business cyber security should therefore be considered as part of an overall approach to practical security management.
Security also has to remain workable after the initial setup. If a process is too difficult to maintain alongside normal business responsibilities, it is unlikely to provide much value over time. Axiom Defender small business cyber security remains most relevant when the support fits the business’s actual needs, resources, and ongoing security responsibilities.
One thought on “Axiom Defender Small Business Cyber Security: How It Supports Your Business”